Episode 14 · · 24 min
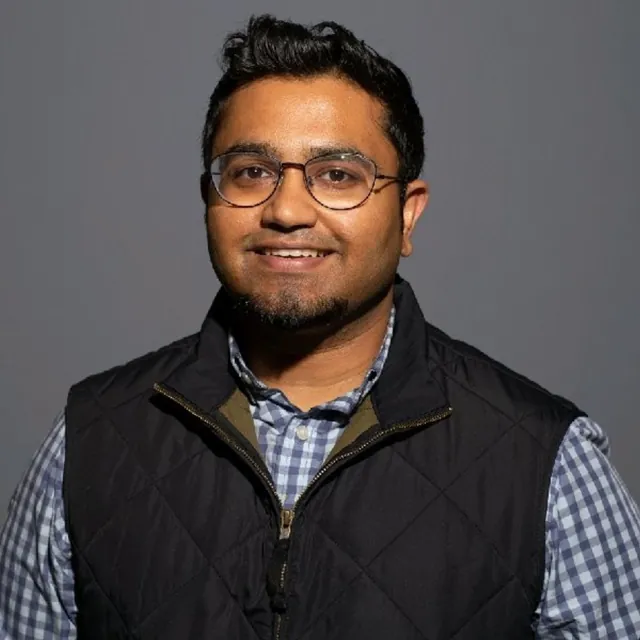
Nipun Gupta From Security Consultant to Security Innovator
Cyber security innovation specialist (Vice President) at a large multinational financial institution
Episode summary
Nipun graduated during the recession, but found a job as a consultant which helped him gain experience quickly. He was in fact discouraged to pursue a career in information security due to his immigrant status. Nipun is now a Cyber Security Executive focused on innovation.
BIO:
Nipun Gupta is a Cyber Security Executive at a large global financial institution focusing on innovation. Armed with many years of experience helping Fortune 500 companies solve cyber risk challenges, Nipun is tasked to help his employer discover, adopt, access new cybersecurity solutions protecting against emerging threats.
In the past two years, Nipun co-founded and ran the global Cyber Innovation Ecosystem strategy at a global consulting company with a specific focus on US and Israeli startups. He offers a strong network of security executives, startup founders, and the Venture Capital community in the West Coast and abroad. Technically proficient in network and application security, Nipun is a trusted advisor for many financial service institutions, technology, and telecom companies contributing to solutions worth tens of millions of dollars. Nipun completed his Masters of Information Technology and Information Security at Carnegie Mellon University, and has been collecting industry certifications like CISSP and SABSA ever since.
Notes:
Was discouraged to go into cybersecurity due to his immigrant status
Graduated in a tough time during the 2008 recession
Discusses burnout and having to work odd hours for 6 months of the year
The show "24" was an influence in sparking the interest in information security
Shares an interesting war story where he accessed tons of files
Discusses the personality traits needed to be a consultant
Quotes
"The biggest problem security professionals will continue to face is how to bridge that gap between technical conversation and business conversation."
"You have to be technical to understand the depth of the issue, but at the same time, you need to be able to express it in business language so non-technical people can make those decisions."
"I think you have to talk in terms of risk. Every business professional [in a] large or small company understands risk because risk can put them out of business."
"While I'm an introvert when it comes to working, I'm an extrovert when it comes to expressing my work-related conversations or expressing my work-related issues."
Before infosec: Security consultant at PricewaterhouseCoopers doing red and purple team testing
Chapters
- 0:00
Intro: Nipun Gupta and the journey ahead
Ayman introduces Nipun, who was discouraged from infosec early on, with teasers on consulting and communication.
- 1:38
Today's role: finding security startups for a bank
Nipun describes his innovation job and why buyers lean on big vendors that rarely innovate.
- 3:12
A master's in infosec and being told immigrants cannot get in
He recalls people predicting he could not find work without clearance, and why he disagreed.
- 5:12
Landing a first job at PwC during the recession
Nipun graduated around 2009 when jobs were scarce and consulting firms were hiring for cybersecurity.
- 6:22
Why consulting speeds up your learning
He explains how consulting exposes you to executives and what traits help you get hired, such as being an extrovert.
- 9:05
Burnout, night testing and the technical-to-business gap
He describes about six months of night and weekend testing and why bridging technical and business language is hard.
- 12:13
War story: guessable shared-file links
Nipun reverse engineered sequential public share URLs on a cloud file-sharing app and found thousands of files, including an unreleased binary.
- 14:29
Telling a client their baby is ugly: talk about risk
He explains how to frame cross-site scripting and similar flaws in terms of reputation and data exposure.
- 15:43
Youth: the show 24 and hacking campus Wi-Fi
Nipun cites the TV show 24 as his inspiration and recalls spoofing MAC addresses to get online with multiple devices.
- 18:51
Advice and resources for getting started, including from India
He recommends staying technical early, using Kali Linux and CTFs, securitytube.net, Hak5, and local conferences.
- 21:17
Many roles in security and a LinkedIn guide
Nipun points to his LinkedIn guide and notes that his company's 500 security staff include very few pentesters.
- 23:05
Closing plug for Ayman's new community
Ayman thanks listeners and invites them to join a new community linked in the show notes.
Key takeaways
- Learn to translate technical findings into business risk, such as reputation damage or exposed customer data, so leaders can act on them.
- Consider starting in consulting, because you learn quickly by working with executives, boards and engineers on real problems.
- Be as technical as you can early in your career, since you will need that depth later when you explain findings in business language.
- Build skills with a Linux machine, Kali Linux, Metasploit and Capture the Flag events, and join a university hackers club or CTF team if you can.
- Do not assume you must be a coder or pentester; security also needs project managers, operations staff and executives.
- Look for local security conferences and government jobs in your own country instead of assuming you must work in the US.
Notable quotes
the biggest problem security professionals will probably continue to face is how to bridge that gap between technical conversation and business conversation.
Every business professional, large or small company understands risk because risk can put them out of business.
Biggest advice I have for you is be as technical as you can early on because later on you won't be able to.
Questions answered in this episode
- How did Nipun Gupta get into cybersecurity?
- Nipun was inspired by the TV show 24 as an electronics engineering undergraduate in India, then did a master's in information security in the US around 2008 to 2009. Despite warnings that immigrants could not get security jobs, he landed his first role as a consultant at PricewaterhouseCoopers.
- Is consulting a good way to start a career in cybersecurity?
- Nipun recommends it because you learn on the job how to report to boards, explain issues in business terms and work with engineers. The tradeoffs he mentions are long hours, including nights and weekends for testing, and a personality that suits client-facing work.
- Do you need to be technical to work in information security?
- Nipun says being technical early on is valuable, but it is not required for every role. His employer's roughly 500 security professionals include operations staff, project managers and executives, and very few pentesters.
Show notes and links
Show the original episode notes
Nipun graduated during the recession, but found a job as a consultant which helped him gain experience quickly. He was in fact discouraged to pursue a career in information security due to his immigrant status. Nipun is now a Cyber Security Executive focused on innovation.
BIO:
Nipun Gupta is a Cyber Security Executive at a large global financial institution focusing on innovation. Armed with many years of experience helping Fortune 500 companies solve cyber risk challenges, Nipun is tasked to help his employer discover, adopt, access new cybersecurity solutions protecting against emerging threats.
In the past two years, Nipun co-founded and ran the global Cyber Innovation Ecosystem strategy at a global consulting company with a specific focus on US and Israeli startups. He offers a strong network of security executives, startup founders, and the Venture Capital community in the West Coast and abroad. Technically proficient in network and application security, Nipun is a trusted advisor for many financial service institutions, technology, and telecom companies contributing to solutions worth tens of millions of dollars. Nipun completed his Masters of Information Technology and Information Security at Carnegie Mellon University, and has been collecting industry certifications like CISSP and SABSA ever since.
Notes:
-
Was discouraged to go into cybersecurity due to his immigrant status
-
Graduated in a tough time during the 2008 recession
-
Discusses burnout and having to work odd hours for 6 months of the year
-
The show "24" was an influence in sparking the interest in information security
-
Shares an interesting war story where he accessed tons of files
-
Discusses the personality traits needed to be a consultant
Quotes
- "The biggest problem security professionals will continue to face is how to bridge that gap between technical conversation and business conversation."
- "You have to be technical to understand the depth of the issue, but at the same time, you need to be able to express it in business language so non-technical people can make those decisions."
- "I think you have to talk in terms of risk. Every business professional [in a] large or small company understands risk because risk can put them out of business."
- "While I'm an introvert when it comes to working, I'm an extrovert when it comes to expressing my work-related conversations or expressing my work-related issues."
Links:
- Nipun on Twitter: https://twitter.com/nipungupta
- Nipun on LinkedIN: https://www.linkedin.com/in/guptanipun/
- SecurityTube: https://www.youtube.com/channel/UCBRNlyf9lURksAEnM-pyQdA
- Hak5: https://hak5.org
- Nullcon: https://nullcon.net
- BayThreat: http://baythreat.org/
- Intro Music - "Cascadia" by Trash80: https://trash80.com/#/content/133/weeklybeats-2012-week5
- Outro Music - "Put This Rap Together
" by Bobby Cole: https://www.audioblocks.com/stock-audio/put-this-rap-together%C2%A0-98857.html
See omnystudio.com/listener for privacy information.
Mentioned in this episode:
Full transcript
Transcribed from the episode audio. Spoof ads (Ayman's parody commercials poking fun at the industry) are marked.Download .txt
Welcome to Getting Into Infosec. I'm your host, Ayman Elsawah. Today, my guest is Nipun Gupta. Nipun shares how he got into infosec and in fact, at some point was actually discouraged to pursue the field.
Even before that, when I was doing my master's, a lot of people discouraged me to go into this industry.
Nipun spent most of his career as a consultant, which provided him an accelerated growth.
Because most of the learning we do is on the job, as you can probably agree with me as well. There's not a school that would teach you how to respond to the board, how to report cybersecurity issues in a way that they're understandable, how to talk to engineers who have, you know, never really dealt with security professionals before.
He also shares with us an interesting war story, but also emphasizes how important communication is in information security.
The biggest problem security professionals will probably continue to face is how to bridge that gap between technical conversation and business conversation. Because you have to be technical in order to understand the depth of the issue. But at the same time, you need to be able to express it in business language so that non-technical people can make those decisions.
I originally met Nipun at the now defunct Baythreat conference. Baythreat was a local conference that had both defensive and offensive tracks. So it was really interesting to see that. I would like to see more of that at other conferences as well.
All right, on to the show.
Hey, Nipun, thanks for coming to the show.
Hey, thank you for having me.
All right. So this is the first time we're doing an in-person interview.
And I must tell you, what a great setup.
Oh, thank you. Thank you. Yeah. So lucky to have someone nearby in security to do this over. Anyway, so walk us through what you do today and maybe a little bit of how you got into information security.
Sure. I actually work for a large multinational financial corporation and I work as a cyber security innovation specialist. And my title is vice president, if that means anything. I'm a financial analyst, like a middle manager sort of title.
Yeah, there's often a lot of vice presidents in banking, financial.
Yeah.
Okay. And what do you have to do from a cybersecurity perspective?
Yeah, so I think this is the coolest job on the planet Earth, especially in cybersecurity. Yeah, I was in cybersecurity consulting before I joined the bank. But now since I've done this, my only job is to find interesting, cool, innovative technology startups and see how we can use them at the bank.
Okay. Because banks traditionally don't move that fast from using cybersecurity technology. Is that right?
Yeah. I mean, this is not just limited to the banks. I think banks are the most innovation friendly because they're the most mature when it comes to cybersecurity. But if you look at cybersecurity industry in general, most of the buyers prefer to buy from large, well-known, well-marketed vendors out there. Which I think is a cardinal sin when it comes to buying good technology, because most of the big security vendors don't innovate all that much. And especially when you're looking at emerging security threats, their products cannot handle that very well.
Okay. So tell us how you first got into security.
Yeah, I actually came to the US after a first semester in Japan. So I did my master's in information security, as it was called back then. And that started my official foray into information security. Before that, I did like a major project. That's how we call it, like a minor and a major project in my undergrad. It's not really totally dedicated to cybersecurity, but it was like, you know, periphery related to that. So we had to triangulate locations of people in dorm rooms using the Internet. So I was able to do that with the error of like plus minus five meters. Oh, nice. Yeah.
Nice. Using just open source?
Using open source tools like MATLAB and simulation techniques.
Okay.
Okay.
Great. And how was it when you were trying to enter the workforce?
Yeah, I think even before that, when I was doing my master's, a lot of people discouraged me to go into this industry. Although I was like extremely interested to, you know, be a cybersecurity professional. Everybody was like, oh, hey, you are an immigrant. So I was in India when I was applying for this degree. And people were like, okay, you're not going to find a job because most of the jobs in cybersecurity are for U.S. citizens. You're going to go and work in the U.S., right? And, you know, even during my degree, people who were not in my degree always used to be skeptical of me ever finding a job. Oh, wow. Yeah. Yeah. They were like, hey, you are going to at least need a permanent residency, if not a citizenship, because you can then find a clearance and then you can work for government related projects.
And I could not believe that because, you know, every single company needs cybersecurity, not just the government.
Right. Yeah. Right. Is there still that mentality today?
I haven't interacted with the students recently, but I think it's changing, right? When so many news items indicate that corporations are getting hacked, public and private, you know, so it's definitely a non-government problem as well.
Yeah, it's a much different time now that cybersecurity is really in the forefront of the news and everything like that. Okay, so you had a lot of naysayers when you were in your program. And so when you graduated in your program, how did you get your first job?
Yeah, it was actually an interesting time, although I think I was lucky to be in cybersecurity because this is 2008-9 timeframe when I started doing my degree. Okay. So jobs were generally not available, right?
Right, the recession and everything.
Yeah, the recession hit, US job market really went down, limited jobs, even more limited for immigrants because they had to sponsor green card and so on and so forth. So I think cybersecurity was just the need of the hour for many of the corporations. And they were paying other consulting companies to come and tell them the issues and solutions and so on and so forth. So I got my first job in cybersecurity at a consulting company called PricewaterhouseCoopers, which was a great experience because I had no clue how practically the cybersecurity enterprises worked or organizations in large enterprises worked. And it was actually a very dismal state in my experience, especially at most Fortune 500s.
And being a consultant gives you a tremendous amount of experience in a very short amount of time, right?
Yes, yes. That's like the best part of a consulting job. You are interfacing with high level directors, even chief executives of many, many large corporations who have worked in the industry for more than 10, 20 years. So you're attracting very experienced professionals. Who may or may not know much about cybersecurity, but they're trusting you to do their job. So it's kind of imperative for you to know the theory and learn from people who have worked in this industry for a long time. And you get to interact with them, you get to understand real world problems they are facing and how they report concerns to their board and you help them do that. So it was extremely fulfilling and learning at the same time.
Okay. And you've been a consultant, I guess, a majority of your professional life. So would you recommend to those new to information security to seek a job in the consulting space?
I think so. I think that's a really interesting way to start your career in cybersecurity. Because most of the learning we do is on the job, as you can probably agree with me as well. Because there's not a school that would teach you how to respond to the board, how to report cybersecurity issues in a way that they're understandable. How to talk to engineers who have, you know, never really dealt with security professionals before. So I think these are probably the more critical parts of the job that you learn only in something like consulting. Okay.
And what does it take to get a job in a consulting company?
I think you have to be an extrovert, first and foremost.
An extrovert?
An extrovert, yes. So if that is the part of your personality, it's definitely simpler for you to get a job there. For me, it was as easy as having a company come to my career fair, then shortlisting me from a pool of candidates for a more privately organized party or dinner, which was for shortlisted candidates. And then we went from that process to interview. What are they looking for? They're looking for people who can represent the brand that they carry when it comes to professional conversations with business leaders in the world. More polished, you have to have a certain kind of personality to be able to talk the talk, the business talk, you know, and a lot of our security engineers have this drawback of being an introvert.
It's a drawback in the consulting industry for sure. And especially when it comes to interacting with business leaders, because they're looking for Numbers more colorful conversations than just like you know you have a vulnerability okay they're looking for assurance they're looking for assurance they're looking for more context specific understanding of whatever security issues we find or we want to resolve okay yeah
Cool. So what about the less thankful, less rewarding times in the consulting space? Because there's a lot of burnout, wouldn't you say? I think a lot of people only stay, what, two or three years before they move on. From your perspective, can you talk more about that?
Yeah, the less exciting times in security. So now I work for a large company, so I can understand the blue team perspective. But I was primarily in the reddish purplish team before I got here. So I think the biggest issue is that you don't want to do security testing in regular business hours, especially if your business depends on those assets that are being tested. So which means that as security professionals, if you are doing the testing, you'll have to Work on the weekends or work overnight which i have done a lot in my life for some reason i think if i total it up probably around six months of my professional life i was doing either night testing or weekend testing oh wow so that i think is not so glamorous and at the same time it is stressy very stressful okay yeah and what about like the hours and the culture and things like that
Yeah, so I think the biggest problem security professionals will probably continue to face is how to bridge that gap between technical conversation and business conversation. Because you have to be technical in order to understand the depth of the issue. But at the same time, you need to be able to express it in business language so that non-technical people can make those decisions. Okay. So as a security professional, you need to maintain that balance and be that translator. I think that has caused a lot of issues in my life in the past. Like sometimes myself, sometimes my colleagues have done that where they become too technical or they keep stressing that this is an issue without properly expressing the concern in the language that a business leader can understand.
Do you have an example maybe you could share while protecting the innocent?
Yeah, of course. Cross-site scripting as an example. Sure, cross-site scripting is a huge, big flaw in an application. But unless you can tell me what cross-site scripting can cause my application to do or how it can be harmful, it's not useful. Unfortunately, our, you know, literature and most of the cross-site scripting related tools which can find those or testers who can find those end up writing the report of this is a huge flaw. It's all asked top ten, you know, but there's not a very good description of how it can affect your application. So unless you're a smart professional, you can't express it because you haven't been able to find it in any like Google researches that you did.
So the impact is not clear.
The impact is not clear and the business leader is like, okay, yeah, we'll just push it to one of those low priority items on my list. But it's imperative for a professional to express that, hey, cross-site scripting can lead to defacement of your web application. It can lead to administrative access to the server of where the application is hosted. But I think these are the concerns that are not very easily expressed. Any security professionals fail to express that in the business language.
Okay. Do you have any interesting war stories that you've seen among any of your many clients that you've been to?
I do. I can actually talk about this because this company doesn't exist anymore. Okay. But trust me, security was not the reason they didn't exist. So this was a consulting gig where we had to do security analysis of a cloud file sharing application. Okay. So we went to this client, VP of Engineering, gave us a binary to work with, as well as the web application URLs. So the idea was find, you know, we did some threat modeling and we tried to find ways that somebody could get unauthorized access to a file that has been shared in the past. So in this investigation. I was able to reverse engineer the URL itself that is being used for sharing. So let's say I and you are trying to share a document amongst each other and I ended up sharing it to public, but I just send you the link because that's the easier way of doing it.
Otherwise you have to make an account and you have to be on the same shared folder. So I just shared it with the public. The link has no expiration date.
Oh, okay.
Right. And I am not notified that it won't expire ever.
Oh, okay.
And guess how the sequencing is created?
Oh, sequentially?
It's the timestamp and the date and the sequence number of the files in your folder. So it's one, it's number one, it's two, it's number two, right? So basically for any given timestamp and date, you can find any file that was shared ever. So you just run the sequence and do a base64 and then you get the URL. So we Googled this exact formula and guess how many files we found?
Oh boy.
A lot. So yeah, thousands of files we could basically download, which were not meant to be shared with the public. But the effect was huge. The impact of this vulnerability was huge. The funniest part was we actually downloaded the binary that was not supposed to be released from the VP's own shared folder. Oh, nice. Yeah, that was not a great conversation when we presented this to them.
Wow. Yep. Didn't take a while.
No, I think they didn't realize that this is how their product can be abused.
Okay. So tell us about like, you know, how sometimes you have to explain to customers that their baby's ugly. How do you do it in the nicest way possible?
I think you have to talk in terms of risk. Every business professional, large or small company understands risk because risk can put them out of business. So anytime you can either quantify or qualify a risk in the terms they can understand. So let me give you an example. Going back to that cross-site scripting. If the website's look and feel is important to the reputation of their business, definitely that's the part you want to express this issue as. This can cause harm to your reputation because the website can be defaced by exploiting cross-site scripting issue. So that's number one. And that's probably the more innocuous way of harming the website. Another one is a worse way is if they get access to the server, personal data of their customers, which may have financial data of their own company, employees, so on and so forth.
I think that's the other thing that they probably understand a little more easily if you express it in those terms, that this is the data that's at risk. If stolen, this data can be abused and the company can be put at risk because reputation can be affected.
Okay. So let's change gears for a little bit and talk about the younger Nupun. How was your youth? What was your exposure to technology? And what made you want to do information security?
So I think I have answered this question many ways, but if I'm being honest with myself, it was the show 24. Oh, okay. Yes. So in 24 season two, Zachary Quinto plays the role of the offensive slash defensive hacker for the counterintelligence unit, CTU, in that show. And I was just ecstatic when I saw him play that role. I really identified with that character because while I'm an introvert when it comes to working, I'm an extrovert when it comes to expressing my work-related conversations or expressing my work-related issues. So I thought that was a great role. While he's not in the field hunting down terrorists, he's actually helping the field agents do that by hacking into buildings, Opening the doors right when the agent on the field needed it.
Finding plans to buildings and finding bank accounts where illicit money has been stored and things like that.
How old were you when you saw that?
It was like early years of college, probably 19. Okay.
Yeah. So you're still doing your undergrad in some sort of technical capacity? Yeah.
Yeah, it was an electronics engineering course.
Okay.
Yeah.
And then you got that itch for security and you decided to do that master's in... Yeah, I thought that was such a cool thing.
And the only security courses online were how to make a virus, how to annoy people, basically.
Is there any time in your youth you hacked something?
I think so. It's a very simple one. But even in my college, we had access to Wi-Fi. So Wi-Fi was a new thing in my college back in that time. This is like 2006, circa 2006. So Wi-Fi just came to our university campus. Everybody was excited. But the only way to access Wi-Fi was if you would register your machine with the university authorities. And how do you register that? You just give them your MAC address.
Right, that's it.
Yeah, white listed MAC addresses, right? So nobody who is not part of the university could not access the university Wi-Fi. You know, funny thing is they limited your usage to just one device, but some of us had more than one device, right? So the way you do that is you would just run MAC address simulator and basically fool them to believe, oh, this is the same exact device on other devices. Yeah. So I would say this is like the only hack I've tried where I would get access to the internet on every single device. While most of the other people probably in my dorm, I know that struggle. Okay.
Okay. Yeah. You saw a problem and you said to yourself, there's got to be another way to get around this. Yep. Exactly. What kind of computer did you have growing up?
So I know my dad had Windows 3.1. That was the first laptop he ever brought home. Okay. I didn't have a computer until I was like mid-teens. That's when we bought like a Windows 95 machine. Yeah, it's like a Pentium 2, I think.
What is some advice that you can give to anyone basically looking to get into information security today?
Biggest advice I have for you is be as technical as you can early on because later on you won't be able to. You'll have to express your security findings, security concerns in business language. And for that, you need to understand the depth of technical work. With that being said, it's not necessary for you to be technical in security because there are many new fields cropping up like security project management, where you're just coordinating schedules of the people in security as well as helping run the projects. You don't need to be technical. You need to just understand basic levels of information security knowledge. Yeah. So I would say get a Linux computer, mess up with Metasploit, try playing around with Kali Linux.
These are some of the attack distributions out there. Play Capture the Flag at any opportunity you get. Join your university hackers club, university Capture the Flag team if you have it. If not, try to take a course. I think securitytube.net is a website you could understand some basics of security at. I wish I had access to that when I was my undergrad.
Right. There's so many resources right now that just weren't available before. So it's really amazing. Okay, great. So anything specific to those maybe overseas, say in India or anywhere, you know, those trying to get into infosec, are there any particular resources they can look into?
Yeah, I think a couple of them I mentioned already. I think there's so many good YouTube videos now who can teach you a hacker's perspective of a security professional. Hack5 videos are great. Darren Kitchen, amazing, cool teacher. And you can also go to local security conferences. I think this is some trend that I've seen recently. Every country has their version of Black Hat, RSA. Their companies focused on security are there, so you can find local employers there. You don't need to be in the U.S., To practice information security. Every country has a security problem today. You can find your local government jobs. That's always an option. You can be part of the offensive, defensive workforce there, learn a lot more advanced techniques in security.
And I think if you're in India, you should definitely go to Nalcon. A lot more diverse now, a lot more international presence at Nalcon recently. It happens in Goa every year. So if you're looking for Miami in India, that's where you go.
Yeah, Goa is a beautiful place.
Yep. Yeah, I've been there.
So Nipun, what would you recommend to folks looking to get into the information security field starting out?
Yeah, I think it's hard to give you all the advice in the podcast, but I would recommend listeners to check out my LinkedIn post on how to get started in cybersecurity. So there are a few jobs that you can get. It doesn't necessarily need to be a security engineer or security consultant. There are some other jobs as well, but all of them require some level of security knowledge. And I've actually linked to places where you can get, most of them are like freely available on the internet. So you don't need to pay for anything. I've tried to take care of the paywall if there is any. So there's nothing. Most of them are very easy to access. So you can go and get started in information security. And it really describes if you're just an executive looking to learn, you know, you don't need to go deep.
You don't need to be technical. You have these levels of knowledge that you need to get. And accordingly, the description has details in it.
Okay, yeah, something for everybody, basically.
Yeah, something for anybody who wants to learn more about cybersecurity.
Depending on where they want to go, because the field is big, right? It's not just being a pen tester.
Yeah, so our company has around 500 security professionals. Not all of them are pen testers. Actually, very few of them are pen testers. A lot of them are operations people. Some of them are project managers. One of them is an innovator.
Innovate, right?
Yeah, and a lot of them are just executives reporting the right information to the right people. Okay.
There was even a controversial post on Twitter lately about if you don't know how to code, then you're basically useless or shouldn't be in the security industry. I don't know if you saw that or not.
That sounds like a very false statement.
Well, Nipun, thank you so much for coming on the show and taking the time to share your experience.
Thanks for having me.
All right.
Thank you.
Hey, thanks for listening. So I built a lot of things and I'm building something new. I'm working on a new community. I want to bring everyone together with all the things that I've done into just one space. So I'm really excited about it and would love to stay in touch and get some early adopters or feedback. So check out the link below in the show notes and send me a hello. And that's about it. I hope you're having a wonderful day. Thanks. Talk to you soon.